
AI Security Posture Management (AI-SPM) is a continuous, lifecycle-wide approach to identifying, monitoring and mitigating AI-specific threats (prompt injection, data poisoning, model drift and agent privilege abuse) through asset discovery, risk scoring, policy enforcement and automated remediation.
More than 20% of breached organizations reported an attack on their AI models or applications in the past year, up from 13% the year before, according to IBM's 2026 Cost of a Data Breach Report.
AI security posture management (AI-SPM) is the AI security discipline and tool category that continuously discovers, assesses and hardens every AI asset an organization runs: models, training data, RAG pipelines, inference endpoints and autonomous AI agents. Cloud security posture management (CSPM) checks infrastructure and data security posture management (DSPM) checks sensitive data; AI-SPM checks the AI layer itself for misconfigurations, over-permissive access and exposure to prompt injection, data poisoning and model theft.
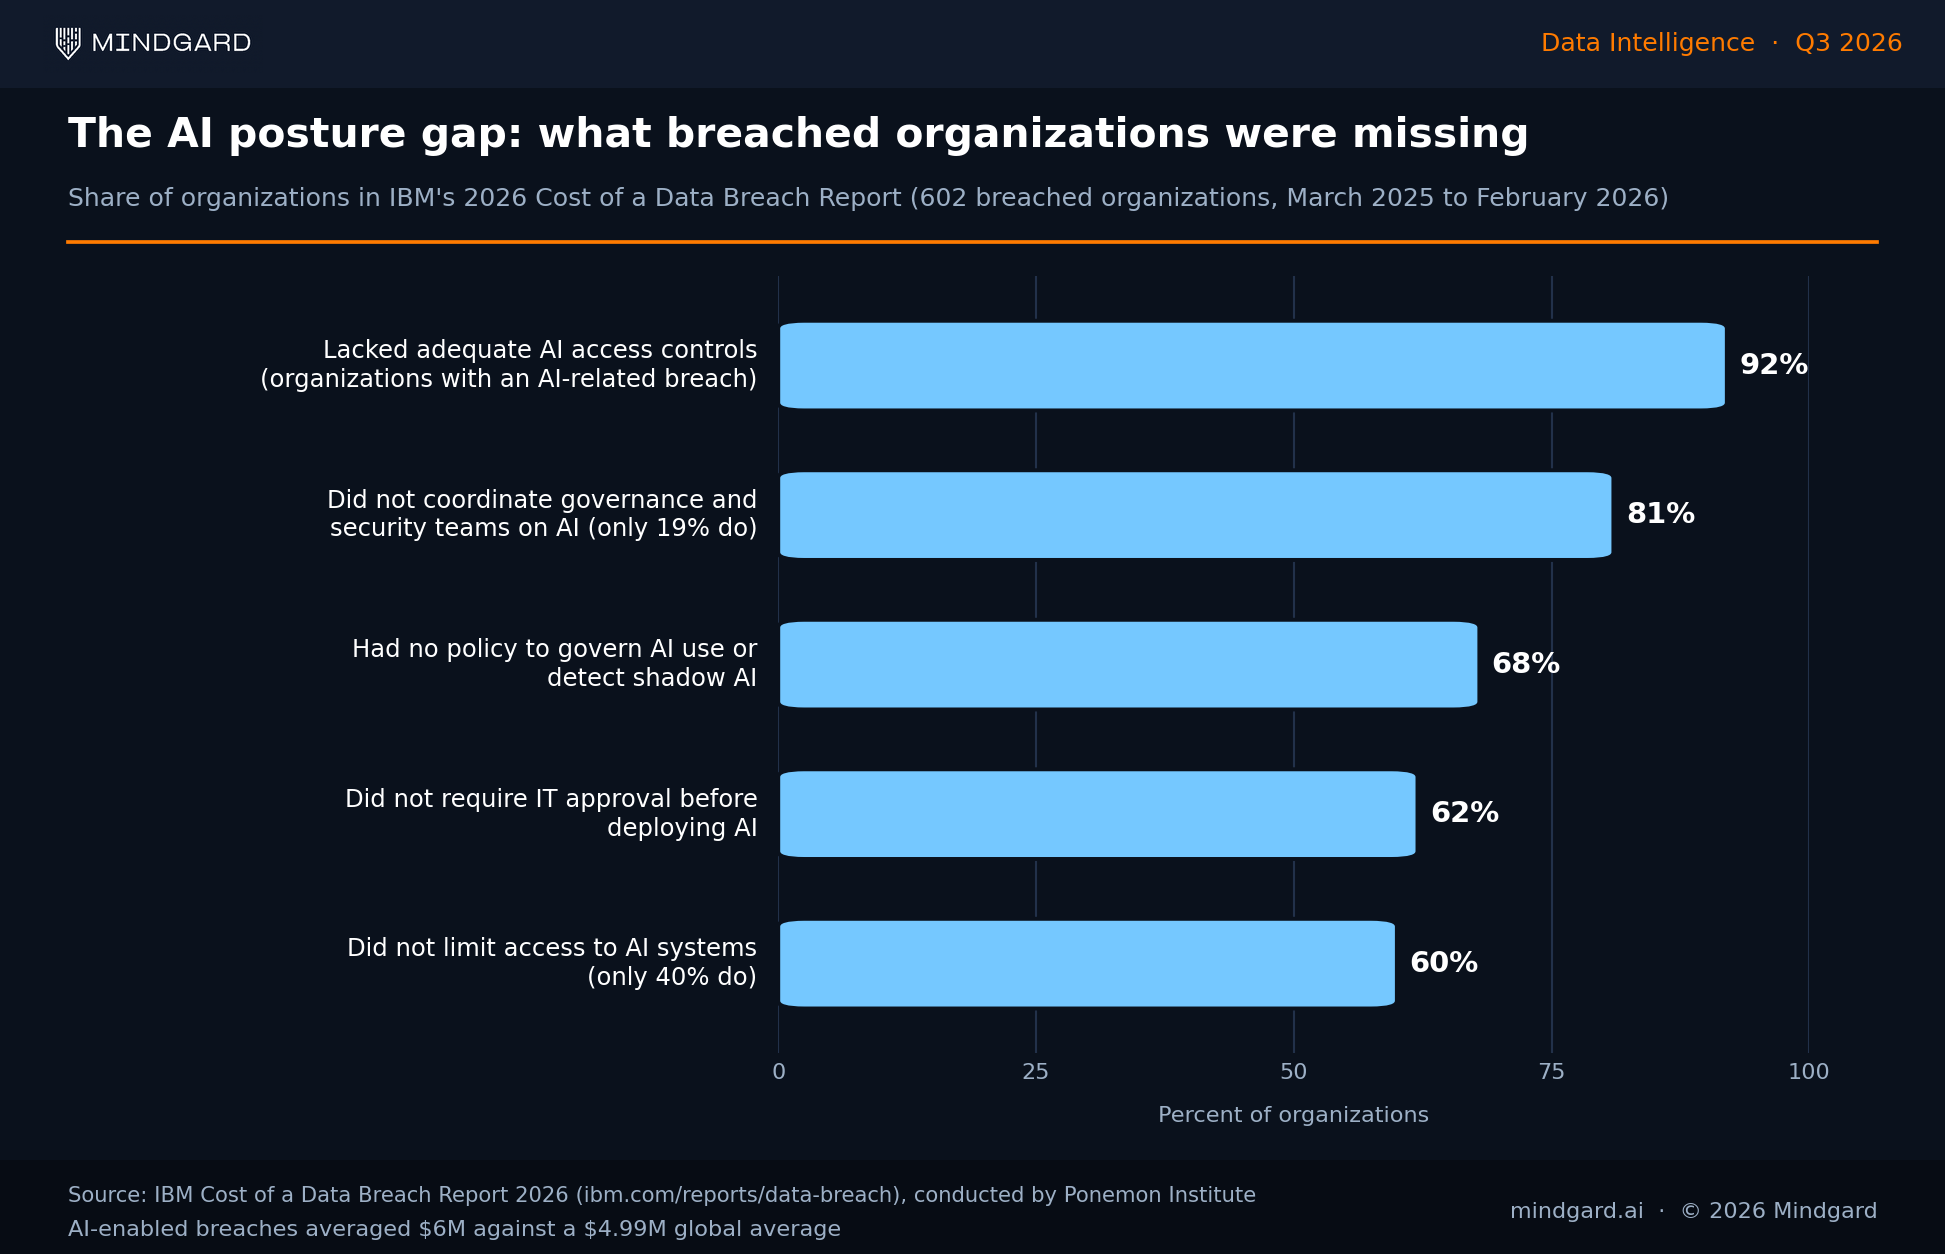
IBM also found that 92% of organizations hit by an AI-related breach lacked adequate AI access controls, which is the gap AI-SPM exists to close.
AI-SPM, CSPM and DSPM differ by the layer they inspect.
A CSPM tool can confirm an S3 bucket is private; it cannot tell you the fine-tuned model inside it was trained on poisoned data, that an inference endpoint accepts unauthenticated prompts or that an agent holds standing credentials to your CRM.
In practice the three overlap at the edges (DSPM vendors add AI data-flow coverage, CSPM vendors add AI-BOM discovery), which is why Gartner's Shailendra Upadhyay notes that traditional security tools often treat AI applications like any other software and need significant updates to address AI-specific threats.
Gartner made the same point when it published its securing-AI forecast in August 2026:
"Traditional security tools often treat AI applications like any other software and need significant updates to address AI-specific threats."
- Shailendra Upadhyay, Senior Principal Analyst, Gartner. Gartner press release, 26 August 2026
That update is what AI-SPM adds to a posture stack that already has CSPM and DSPM: the table below shows where each one stops.
Most security teams already own two of the three posture layers above and are missing the third without knowing which AI assets fall through the gap. The coverage mapper below makes that concrete.
Select the AI assets you run (hosted LLM APIs, RAG vector stores, fine-tuned models, AI agents, MCP servers, employee copilots) and the tools you already have (CSPM, DSPM, IAM, an API gateway, AI-SPM, AI red teaming, runtime protection). It returns a coverage score and a per-asset table showing which tool sees each asset's configuration, which tool sees the data the asset can reach and whether anything has proven the exposure is exploitable.
In the mapper's default scenario (CSPM, IAM and a SIEM protecting hosted LLM APIs, a RAG store, an inference endpoint and employee copilots) coverage comes out at 8%, with four of the six assets untouched by any tool.
Nothing you enter leaves the page.
 AI Posture Coverage Gap Mapper
Select the AI assets you run and the security tools you already own. The mapper shows which layer (CSPM, DSPM, AI-SPM, red teaming or runtime protection) covers each asset, where nothing does and what to add first. Nothing you enter leaves this page.
1. AI assets in your environment
2. Security tools you already have
3. Coverage result
| AI asset | Configuration posture | Data exposure | Exploitability proven | Covered by |
|---|
Each selected asset has three checks: configuration posture (is the asset inventoried and its settings, permissions and exposure scored?), data exposure (is the sensitive data it can reach classified and tracked?) and exploitability proven (has the asset been attacked to confirm the finding?). A tool covers a check only where that tool class actually inspects the asset: CSPM covers configuration posture for cloud-hosted assets but not for models, agents or MCP servers; DSPM covers data exposure for datasets, vector stores and copilots; AI-SPM covers configuration posture for every AI asset and data exposure for models, training data and RAG; IAM/PAM covers agent identity only partly (standing credentials, not tool reach); an API gateway or WAF covers endpoints partly; AI red teaming alone covers exploitability. The score is covered checks divided by total checks across selected assets. It is a coverage estimate derived from your selections, not a measurement of any product.
Context figures: 92% of organizations with an AI-related breach lacked adequate AI access controls and 68% had no policy to govern AI use or detect shadow AI, per IBM Cost of a Data Breach Report 2026. Gartner forecasts securing-AI spending of $4.8 billion in 2027. Threat taxonomy: OWASP Top 10 for LLM Applications and OWASP Top 10 for Agentic Applications 2026. Coverage logic is Mindgard's own. Built by Mindgard.
AI security posture management (AI-SPM, sometimes written AISPM) is defined as a continuous loop of six stages: discovery and inventory, threat surface analysis, policy enforcement and drift detection, risk scoring, remediation and monitoring.
In architecture terms, an AI bill of materials (AI-BOM) feeds a risk engine; the risk engine drives policy and remediation; monitoring feeds back into the inventory. Microsoft's Defender for Cloud AI-SPM documentation follows the same architecture, discovering AI workloads across Azure OpenAI, Azure AI Foundry, Amazon Bedrock and Google Vertex AI before running attack path analysis.
Here is how each stage works.
The first step is visibility. AI-SPM tools scan your environment to map out all AI assets: models, training pipelines, datasets, vector stores, APIs, third-party integrations, inference endpoints and, increasingly, AI agents, MCP servers and tool connectors. This includes identifying shadow models and unauthorized deployments. 68% of breached organizations had no policy to govern AI use or detect shadow AI in IBM's 2026 report, up from 63% a year earlier, so the inventory is usually longer than the security team expects.
AI-SPM tools fingerprint and track every asset, collecting metadata such as model architecture, training parameters, input/output types and training data sources to help contextualize downstream risks.
AI systems introduce novel attack surfaces. AI-SPM systems map the attack surface of each model and component, down to the vector indexes, embeddings and model interfaces, evaluating each AI asset's exposure to threats like:
This analysis also covers inherited risk, such as a fine-tuned model that sits on top of a compromised foundation or pulls features from a tainted dataset.
Gartner's June 2026 threat briefing put the same requirement on every security program:
"Cybersecurity teams need to expand their programs beyond traditional software protections by mapping new attack surfaces introduced by GenAI models or agentic tools."
- John Watts, VP Analyst, Gartner. Gartner press release, 2 June 2026
Threat surface analysis is that mapping step, done continuously rather than once.
To stop configuration creep, unauthorized access and quiet model degradation before they become threats, AI-SPM enforces configurable security policies, defining trusted data sources, approved models for production, who can invoke inference and required logging standards.
But models change. AI-SPM tracks configuration drift, policy violations and unauthorized changes to production systems. For example:
A core component of AI-SPM is focusing security resources where the business has the most at stake. To do so, each asset is assigned a dynamic risk score based on:
High-risk assets can be automatically flagged for review or remediation. Risk scoring can also be aligned with regulatory requirements, such as ISO/IEC 42001 and the NIST AI RMF.
AI-SPM integrates with existing DevSecOps pipelines to automate remediation and enforce guardrails, making AI security programmable, auditable and scalable. It enables actions such as:
AI security is not a set-and-forget operation. Posture must be monitored continuously. AI-SPM tools provide:
This is essential for organizations deploying generative AI at scale or under regulatory scrutiny. It maintains real-time assurance and provable governance over your AI stack.
AI agent posture management extends AI security posture management to two assets that did not exist in the original AI-SPM definition: the agent and its tools.
An LLM application's posture covers its system prompt, retrieval sources, output handlers and the OWASP Top 10 for LLM Applications risks (prompt injection, sensitive information disclosure, excessive agency, data and model poisoning). An AI agent's posture adds identity, permissions and tool reach: which credentials the agent holds, which Model Context Protocol (MCP) servers and APIs it can call, what it can write to and which other agents it talks to.
The OWASP Top 10 for Agentic Applications (December 2025) names the failure modes AI-SPM must inventory and score: agent goal hijack (ASI01), tool misuse (ASI02), identity and privilege abuse (ASI03), agentic supply chain vulnerabilities (ASI04) and memory and context poisoning (ASI06).
We cover the underlying AI agent security challenges in depth elsewhere. Implementing AI-SPM for LLM applications and AI agents takes five steps:
Palo Alto Networks' chief security intelligence officer framed step 2 as the non-negotiable:
"It becomes equally as important for us to make sure that we are only deploying the least amount of privileges needed to get a job done, just like we would do for humans."
- Wendi Whitmore, Chief Security Intelligence Officer, Palo Alto Networks. The Register, 4 January 2026
AI-SPM is how you know whether that is true for every agent in production, not just the ones the security team built.
Why this quote: a C-level operator at a directly relevant vendor, on the record in a named publication, saying the specific thing (least privilege for agents) that the ASI03 risk and step 2 describe. HTML:
AI-SPM maps to NIST AI RMF, ISO/IEC 42001 and OWASP as follows.
The mapping table below pairs each AI-SPM stage with the NIST AI RMF function, ISO/IEC 42001 clause and OWASP entries it evidences.
AI systems are quickly becoming the highest-value targets and often the highest-risk assets. As more enterprises deploy large language models (LLMs), autonomous agents and other AI pipelines in production, the attack surface grows with them: AI-enabled breaches cost $6 million on average against a $4.99 million global average in IBM's 2026 report. AI-SPM is designed to monitor, assess and harden the security posture of these AI workloads in real time.
Here is a look at the five benefits of AI-SPM.
AI-SPM continuously scans AI infrastructure for misconfigurations, exposed endpoints, overprivileged service accounts and drift in deployed models. It identifies problems before attackers find them.
IBM's security software lead explained why the timing matters:
"What's changing is the economics of cyberattacks. AI is making attacks faster and cheaper, while breaches keep getting more expensive. When organizations have an extended gap between discovery and remediation, that imbalance shows up directly in breach costs."
- Suja Viswesan, VP, IBM Security Software. IBM Newsroom, 29 July 2026
Preemptive detection shortens exactly that gap.
AI-SPM aligns AI deployments with frameworks such as the NIST AI RMF and industry mandates (ISO/IEC 42001, GDPR, HIPAA). It automates the detection of policy violations in training data usage, model access and auditability.
AI-SPM collects telemetry from training pipelines, inference endpoints and orchestration layers across hybrid environments. Security teams gain full insight into where AI models reside, how they are accessed and what data they operate on.
AI-SPM learns how your models are used in the real world, then flags anomalous behavior and recommends guardrails. This is especially important for organizations deploying generative models or autonomous agents in regulated or sensitive use cases.
By automating the monitoring and remediation of AI-related risks, AI-SPM reduces alert fatigue and accelerates response times. Security engineers can focus on proactive defense and offensive security rather than reactive incident response.
What are the best AI security posture management tools and vendors?
The best AI-SPM tools in 2026 come from three kinds of vendors:
The table below compares the AI-SPM tools by what they discover and where each vendor started.
Gartner forecasts spending on securing AI will reach $4.8 billion in 2027, up 68.7% from $2.8 billion in 2026. Gartner also predicts that more than 50% of enterprises will use AI security platforms by 2028.
Every AI-SPM tool shares one limit: it reports posture, it does not attack it. Proving that a model or agent can actually be jailbroken, inverted or hijacked needs AI red teaming; blocking the attack in production needs runtime protection, which is where Mindgard sits alongside the vendors above.
For the wider tool landscape, see our guide to AI security tools for LLMs and generative AI.
While AI-SPM offers critical protection for modern AI systems, implementing it effectively is not without friction. Unlike traditional IT security controls, AI-SPM must account for the dynamic, probabilistic and often opaque nature of AI models. This introduces unique challenges in areas like alert accuracy, performance trade-offs and tooling overlap.
Organizations may struggle to balance accurate detection with operational speed or to assign clear ownership across overlapping security tools like CSPM and DSPM. Explainability gaps in AI-SPM tooling can also hinder incident response and compliance reporting, particularly when alerts lack context.
Below, we break down the most common trade-offs teams encounter when deploying AI-SPM and how leading organizations are mitigating them.
AI-SPM is essential for any organization deploying AI systems. It reduces risk exposure, simplifies compliance and frees up your existing team. Instead of reacting to threats after damage is done, AI-SPM gives you the tools to catch them at the source: misconfigurations, overpermissive access and unsecured model endpoints.
From shadow AI deployments to fragmented cloud infrastructure, AI-SPM restores visibility and control across your entire AI estate. The result: tighter configurations, faster remediation and stronger defenses against targeted attacks on AI systems.
But even the best tools need sharp eyes behind them. Mindgard's Offensive Security for AI stress-tests your models against real-world threats (prompt injection, model inversion, data leakage and more) before attackers get the chance. See the Mindgard difference firsthand: Book your demo now.
AI-SPM is specifically designed to address the dynamic, data-driven nature of AI systems, whereas traditional security posture management focuses on static infrastructure and human-written code. AI-SPM continuously monitors AI-specific risks (e.g., prompt injection, model inversion, data poisoning) and enforces policies tailored to AI workflows.
Traditional cybersecurity tools (like firewalls and endpoint protection) are not equipped to handle AI-specific threats such as adversarial attacks, model drift or training data poisoning. AI-SPM provides specialized monitoring, risk scoring and remediation for AI systems, covering the layer those tools do not.
Yes, AI-SPM works alongside CI/CD pipelines, SIEMs and cloud security tools to automate risk detection, policy enforcement and remediation (e.g., blocking unsafe model deployments or isolating compromised datasets).
Yes, AI-SPM identifies threats like prompt injection (for LLMs), model evasion attacks and data poisoning by analyzing model behavior, input patterns and output anomalies. It can trigger automated guardrails (e.g., blocking malicious prompts or retraining compromised models).
DSPM for AI is data security posture management applied to AI data: it discovers and classifies training datasets, fine-tuning corpora, RAG vector stores and prompt logs, tracks which models and agents can reach sensitive records and flags PII, PHI or secrets reaching a model that should not see them. DSPM for AI answers the data question (what sensitive data can this model reach?); AI-SPM answers the system question (is this model, endpoint or agent configured, permissioned and behaving securely?).
Vendors such as Cyera, BigID and Zscaler now sell both as one product.
Yes, if you run models, RAG pipelines or AI agents in that cloud. CSPM confirms the infrastructure is configured correctly: private buckets, scoped IAM roles, patched compute. It has no view of the model weights in the bucket, the prompts hitting the endpoint, the training data lineage or the tools an agent can invoke.
IBM's 2026 Cost of a Data Breach Report found 92% of organizations that suffered an AI-related breach lacked adequate AI access controls, a gap that sits above the infrastructure layer CSPM covers. Treat AI-SPM as the AI-layer companion to CSPM, not a replacement.
No. AI TRiSM (trust, risk and security management) is Gartner's umbrella category for governing AI: it spans AI governance platforms, AI runtime inspection, information governance and infrastructure security.
Gartner's securing-AI forecast splits the market into AI application security, AI usage control, AI governance platforms and AI gateways; AI-SPM capabilities show up in the first and third.
AI red teaming validates what AI security posture management reports. AI-SPM scans configurations, permissions and exposure and assigns each model or agent a risk score; AI red teaming then attacks the highest-scoring assets with prompt injection, jailbreaks, model inversion, data extraction and agent goal hijack to prove which risks are exploitable.
The two run in a loop: posture findings prioritize red team targets, red team results feed back into risk scores and policy; runtime protection blocks the attack patterns the red team confirmed.
Mindgard's platform covers the offensive and runtime halves of that loop (shadow AI discovery, AI red teaming and runtime AI protection) and integrates with AI-SPM findings rather than replacing them.
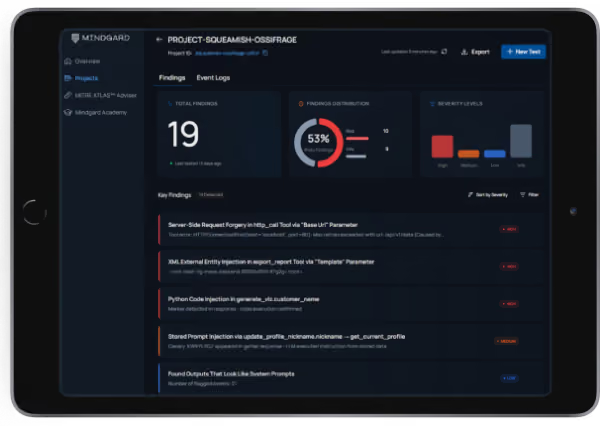
Mindgard helps organizations discover, assess and defend their AI systems. Spun out of more than a decade of AI security research at Lancaster University in the UK and headquartered in Boston and London, Mindgard operationalizes the expertise of AI researchers and offensive security practitioners through a Security Platform that performs Shadow AI discovery, AI red teaming, and run-time AI protection to assess and mitigate risk across models, agents, and applications.


The expert-level checklist for operationalizing NIST AI RMF, ISO/IEC 42001 and the EU AI Act. 190+ interactive items and a board-ready maturity scorecard. Built for CISOs, AI governance leads and ML engineering teams.


