

Contact Us

Mindgard combines world-class research, hacker creativity, and intelligence from 175+ public vulnerability disclosures to continuously strengthen how the platform identifies and stops exploitable AI vulnerabilities.
AI systems don’t exist in isolation. Models, agents, tools, APIs, and data create security blind spots traditional testing cannot see. As these systems become more connected and autonomous, they introduce new attack paths and high-impact risks across the enterprise.


Mindgard operates as an autonomous red teamer, continuously mapping, planning, and executing complex, agentic attack workflows to reveal and reduce real-world AI risk.
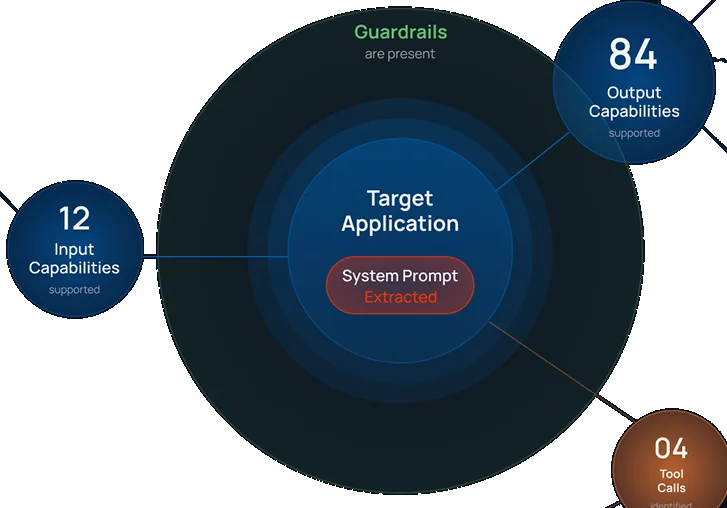
Automate recon & intelligence gathering on AI systems before adversarial testing. Discover instructions, tools, and behaviors attackers can exploit.
Evaluate AI agents for reliability and security and safety weaknesses.
With a single click, Mindgard’s agentic platform red teams AI systems, agents, and infrastructure, emulating real attacker behavior to uncover high-impact vulnerabilities.
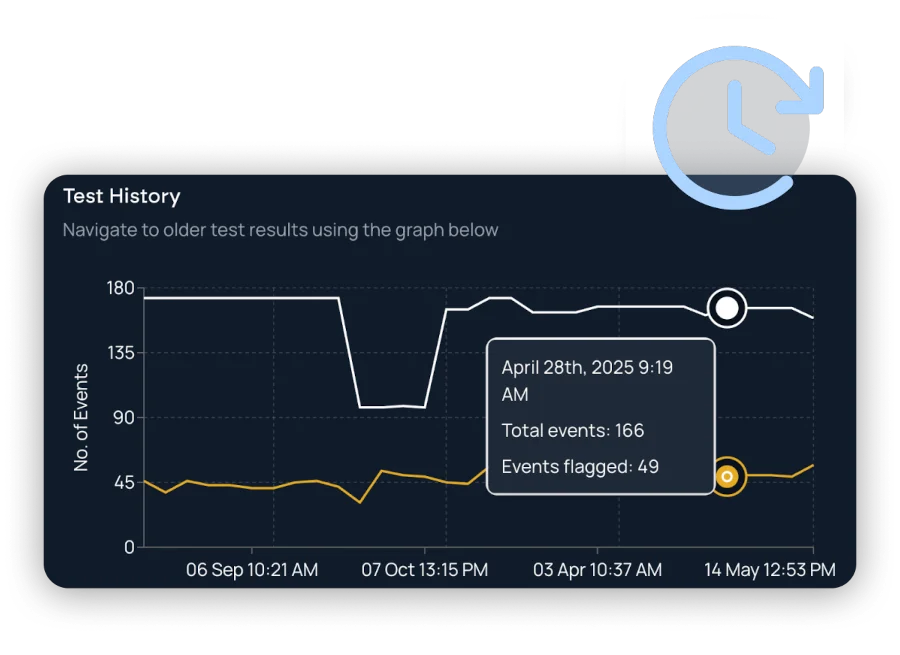
Leverage recon findings to craft attack chains and conduct agentic red teaming.
Continuously map and assess AI risk, validate defenses, and execute AI red teaming at scale, providing clear visibility into vulnerabilities and confidence when reporting to stakeholders and auditors.
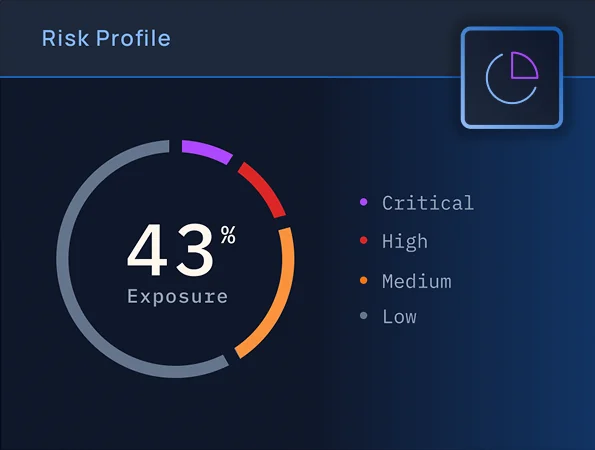
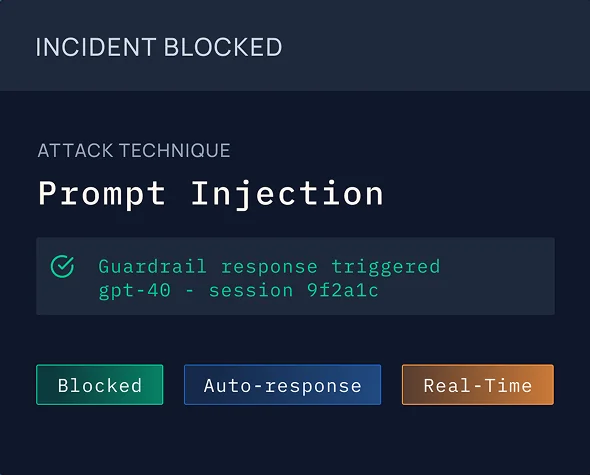
Discover what your AI systems and agents can do, validate where defenses fail, give teams the evidence needed to reduce risk as AI changes.
Identify AI models, agents, MCP/A2A servers, connected tools, and shadow AI within your products.
Reveal the blind spots attackers look for before they launch an attack.
Agentic red teaming uncovers exploitable vulnerabilities and prioritize high-impact risks.
Automatically take action to mitigate risk and validate defensive improvement.
Empower your engineering team to review reports and take action with ease.
Security teams use Mindgard to discover and remediate high impact risk. The platform integrates directly into development and security workflows so organizations can secure AI systems and agents throughout their lifecycle.
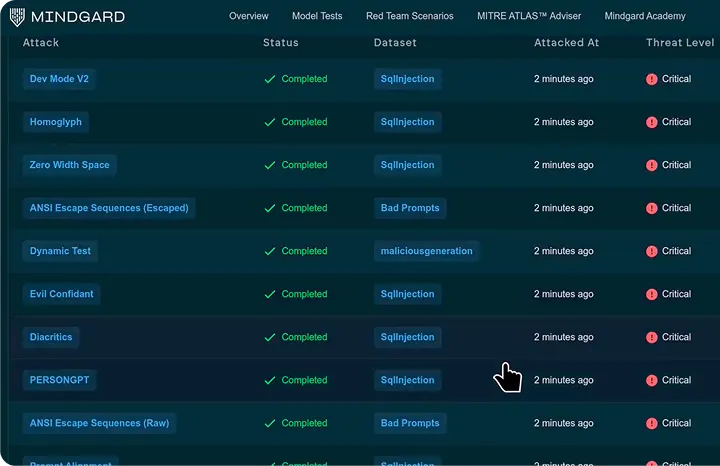

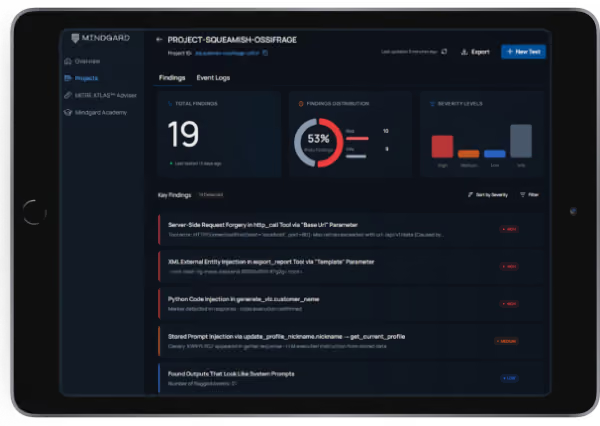
An AI security platform provides evidence of how AI systems have been assessed, which vulnerabilities were proven exploitable, how risks were prioritized, and whether remediation was effective. Mindgard gives security, engineering, GRC, and audit teams reporting they can use to demonstrate that AI risks and controls are being continuously evaluated. This supports evidence-based assurance rather than reliance on point-in-time checklists or self-attestation.
Yes. Mindgard’s AI security platform integrates with development and security workflows through APIs, CI/CD pipelines, ticketing systems, and other enterprise tools. Teams can assess AI throughout development, route evidence-backed findings to the people responsible for remediation, and retest fixes within existing processes. This brings offensive AI security into the software lifecycle without creating a separate manual workflow.
An enterprise AI security platform should provide coverage across applications, agents, models, data, APIs, and connected tools. Important capabilities include AI asset discovery, attacker-led reconnaissance, adaptive attacks, continuous reassessment, evidence of exploitability, remediation guidance, and integration with existing security workflows. The platform should help teams prioritize vulnerabilities by business risk instead of simply producing more findings or test results.
AI systems change whenever teams update a model, prompt, dataset, tool, permission, or integration. These changes can create new attack paths or weaken existing controls. A continuous AI security platform reassesses systems as they evolve. Mindgard helps teams identify new vulnerabilities, verify that fixes remain effective, and maintain an up-to-date view of exploitable AI risk.
An AI security platform assesses the complete agentic system, including the model, instructions, memory, permissions, data, APIs, connected tools, and MCP or A2A servers. Mindgard’s AI security platform uses reconnaissance and agentic attacks to identify how an attacker could manipulate an agent, access sensitive information, misuse tools, bypass controls, or chain weaknesses together to take unauthorized actions.
Guardrails filter or control prompts and outputs, but they do not prove that an AI system is secure. An AI security platform actively tests whether guardrails and other controls can be bypassed as models, prompts, data, tools, and configurations change. Mindgard shows where defenses hold, degrade, or fail, giving teams evidence of what an attacker can get through and where protections must be strengthened.
Traditional AppSec tools focus primarily on vulnerabilities in code, infrastructure, APIs, and configurations. An AI security platform addresses the additional attack surface created by model behavior, prompts, context, data, tools, and prior interactions. Mindgard complements existing AppSec tools with attacker-led reconnaissance and adaptive attacks designed to uncover AI vulnerabilities that conventional security testing may not find.
An AI security platform can identify risks such as prompt injection, jailbreaks, sensitive information disclosure, system prompt leakage, unsafe tool use, excessive agent permissions, and other weaknesses that allow attackers to manipulate AI behavior. Mindgard’s AI security platform also examines how vulnerabilities can be chained across models, agents, APIs, data, and tools to create high-impact attack paths.
Mindgard is an offensive AI security platform that examines AI from an attacker’s perspective. It performs reconnaissance to understand the target, plans attack paths using proprietary intelligence, and conducts adaptive attacks across models, agents, applications, and connected tools. This enables security teams to find, prove, and remediate the vulnerabilities most likely to create material business risk.
An AI security platform protects AI systems from attack, manipulation, and misuse. An AI-powered cybersecurity platform uses AI to improve traditional security functions such as threat detection, investigation, and response. Mindgard focuses on the security of AI, helping organizations understand how attackers could exploit their AI applications and agents and what they must do to reduce that risk.
An AI security platform helps organizations identify and reduce risk across AI applications, agents, models, data, APIs, and connected tools. Mindgard’s AI security platform applies an offensive security approach, continuously tracking AI systems as they change and testing them as an attacker would. It provides continuous visibility into AI risk and evidence teams can use to prioritize and mitigate exploitable vulnerabilities.
Can’t find the answer you’re looking for? Please chat to our friendly team.
Mindgard secures AI models, agents, and applications against exploitable threats. Spun out of more than a decade of pioneering AI security research at Lancaster University, Mindgard combines offensive security expertise, AI red teaming, attacker intelligence, and automated protection to help organizations discover, assess, and mitigate risk across AI models, agents, and applications.