See why AI and security teams choose Mindgard ahead of PyRIT for visibility into their AI attack surface, measurement of AI risk and active defense of AI Systems.
See why AI and security teams choose Mindgard for attack‑driven testing, visibility across models and agents, and enterprise‑grade controls.
Map the AI attack surface to gain visibility into AI inventory and activity; reveal what attackers can find out about an organization’s AI.
Continuously red‑team models, agents, and apps across the AI lifecycle to measure risk. Assess how attackers can exploit your AI and validate fixes.
Actively defend AI. Enforce controls and policies to mitigate AI attacks at run-time. Stop attackers from breaching AI.
Below is a side-by-side comparison of Mindgard and PyRIT across key capabilities that matter to enterprise security and AI teams. Each category highlights how the two platforms approach visibility, testing, and control differently.
Feature
Winner
AI Risk Visibility
Surfaces high impact AI risks including architecture, integration and intellectual-property vulnerabilities. Works across agents, applications and models, providing full-stack visibility and giving teams earlier, deeper risk discovery than runtime-only inspection.
Tests the specific models, endpoints and applications configured as targets, reporting how each responds to attack scenarios. Does not map broader AI architecture, integrations or attack surface.

Shadow AI Discovery
Surfaces AI asset inventory and hidden AI usage. Detects ungoverned model deployments and unapproved data flows.
PyRIT only tests targets that users explicitly register. It has no asset inventory and does not discover shadow AI or unapproved deployments.
AI Risk Assessment
Delivers continuous and automated AI red teaming across agents, models and AI applications. Identifies real exploitation paths to demonstrate exactly how attackers can compromise AI systems.
Runs scenario-based assessments covering content harms, jailbreaks, data leakage, cyber and scam risks against a configured target. Scans are launched on demand from the CLI, GUI or Python code, versus continuous, organization-wide risk assessment.
Behavioral Science Testing
Models attacker behavior across human, linguistic, and system biases to surface vulnerabilities that static testing and persona-based probes cannot surface. Research-driven attack generation continuously evolves to reflect emerging AI threats.
Offers no dedicated behavioral science model of attacker behavior. Instead, it provides individual attack techniques, including persuasion-based and gradual-escalation attacks such as Crescendo, plus psychosocial harm scenarios.
AI Security R&D Talent
86% of staff on R&D team, 38% hold PhDs. Founded by Professor at Lancaster University. Research pipeline from the UK’s top AI security lab.
Built and maintained by Microsoft’s AI Red Team, which has used PyRIT across more than 100 internal red teaming operations. Backed by a published research paper and open-source community contributors.
Simplicity and Usability
Built for both security teams and AI developers with intuitive dashboards, explainable findings, guided remediation workflows, one-click retesting and prioritized risk scoring to accelerate fixes and reduce alert fatigue.
Offers three modes: a CLI scanner, a Python framework and CoPyRIT, a web GUI for human-led red teaming. Setup still requires Python, environment files and YAML configuration. Building custom attacks assumes comfort writing code.
AI Guardrails
Validates and continuously tests guardrail effectiveness through adversarial attacks. Focuses on measuring, stress-testing and improving guardrails rather than acting as a runtime guardrail itself.
Does not provide runtime guardrails, but tests whether safety systems can be bypassed using jailbreaks, encoding and multi-turn attacks. Guardrail testing must be triggered manually.
Attack-Driven Testing
Continuously red-teams models, agents, and applications through attack-driven testing that covers jailbreaks, data exfiltration, and prompt injection. Supports multi-turn adversarial chains with reproducible results to validate fixes.
Provides a deep library of single-turn and multi-turn attacks, including Crescendo, TAP, Skeleton Key and many-shot jailbreaks. Supports multimodal attacks across text, image, audio and video, and can run garak probes as built-in scenarios.
Runtime Detection & Policy
Provides inline detection and enforcement for prompt injection, sensitive data exposure, jailbreak attempts, and tool abuse. Configurable actions include blocking, alerting, enrichment and integration with existing security controls.
PyRIT has no runtime component. Its scorers evaluate responses during an attack; they do not inspect or block live production traffic.
Enterprise Controls
Delivers enterprise-grade governance with RBAC, SAML/SSO, SCIM provisioning, granular permissions, audit trails and centralized policy management. Enables organizations to standardize AI security testing and demonstrate compliance across teams and environments.
CoPyRIT can be deployed to Azure with Entra authentication, and attacks are tagged by operator and operation for tracking. It lacks granular RBAC, SCIM provisioning and centralized policy management.
Integrations
Integrates seamlessly across developer and security workflows, including CI/CD pipelines, GitHub, IDE hooks, SIEM, ticketing systems and APIs. The first AI red teaming solution with a native Burp Suite integration, enabling red teams to extend attack-driven testing into familiar tooling.
Connects to OpenAI, Azure, Anthropic, Google, Hugging Face, HTTP and WebSocket endpoints, and web apps via Playwright. Integrates closely with Azure services and can run in CI/CD pipelines, but offers no native SIEM, ticketing or security tool integrations.
Deployment Options
Most flexible: SaaS, Private cloud, Customer‑managed. On-prem available for certain use cases.
Self-hosted via pip or Docker, with an option to deploy CoPyRIT to your own Azure tenant. Microsoft also uses PyRIT inside its Foundry AI Red Teaming Agent, which is available only on Azure.
Reporting & Scorecards
Provides comprehensive reporting that connects testing outcomes to business risk. Teams can assess how attackers could exploit their AI, validate defenses, and evidence compliance through detailed scorecards, trend analytics, and executive summaries.
Stores conversations, scores and attack results in SQLite or Azure SQL, with success rates by technique and exports to Markdown, JSON or HTML. Reporting is focused on attack outcomes rather than business risk or executive scorecards.
Support & Partnership
Every customer receives a dedicated success team backed by world-class AI security researchers. Mindgard provides hands-on guidance informed by active attack research, helping enterprises apply the latest insights to their own AI environments and continuously strengthen defenses.
Community support through Discord, GitHub issues and documentation. Microsoft’s AI Red Team maintains the project, but there is no dedicated success team or SLA-backed support for the open-source framework.
Pricing Model
Contact sales for tailored pricing.
Free and open source under the MIT license. Users bear the cost of compute, model API calls (including LLMs used as attackers and scorers) and the engineering time to run and maintain assessments.
Powered by the world's most effective attack library for AI, Mindgard enables red teams, security and developers to swiftly identify and remediate AI security vulnerabilities.
Don’t just take our word for it, see how offensive security teams rate the experience across platforms.
CEO at AI software company
Security Lead at F500 Pharma


Purpose-built features that surface AI security threats that really matter.
Extend offensive testing into familiar workflows. Mindgard’s native Burp Suite integration lets red teams chain AI-specific attacks, validate exploits, and report findings directly within their existing toolset.
Learn More >
Turn findings into fixes with guided remediation workflows. Automatically reproduce vulnerabilities, validate patches, and document risk reduction for auditors and leadership
Learn More >
Test beyond text with coverage for vision, audio, and multi-modal models to uncover cross-channel vulnerabilities that attackers can exploit.
Learn More >
Plug into CI/CD pipelines, IDEs, SIEM, and ticketing systems to bring AI risk visibility and testing automation into every stage of development and security operations.
Learn More >
The world’s most effective library of jailbreaks, data exfiltration methods, and prompt injection chains—curated from ongoing research and field testing to mirror the latest real-world threats.
Learn More >
Align findings to emerging frameworks like OWASP Top 10 and MITRE ATLAS, translating technical vulnerabilities into compliance-ready evidence.
Learn More >View and learn more about Mindgard's features, data handling capabilities, or integration options.

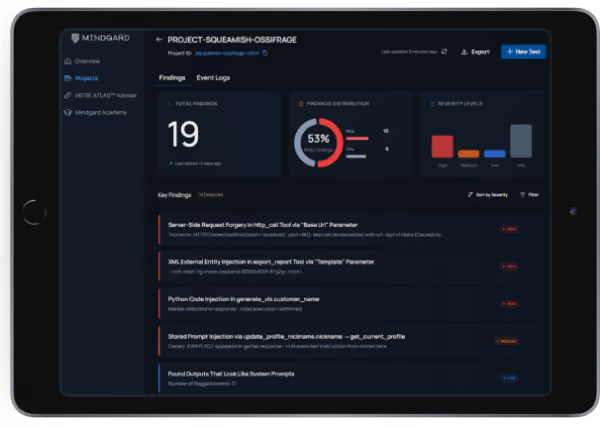
Mindgard secures AI models, agents, and applications against exploitable threats. Spun out of more than a decade of pioneering AI security research at Lancaster University, Mindgard combines offensive security expertise, AI red teaming, attacker intelligence, and automated protection to help organizations discover, assess, and mitigate risk across AI models, agents, and applications.