See why AI and security teams choose Mindgard ahead of Dreadnode (announced as a CrowdStrike acquisition in November 2026) for visibility into their AI attack surface, measurement of AI risk and active defense of AI systems, all from an independent, vendor-neutral AI security platform.
See why AI and security teams choose Mindgard for attack‑driven testing, visibility across models and agents, and enterprise‑grade controls.
Map the AI attack surface to gain visibility into AI inventory and activity; reveal what attackers can find out about an organization’s AI.
Continuously red‑team models, agents, and apps across the AI lifecycle to measure risk. Assess how attackers can exploit your AI and validate fixes.
Actively defend AI. Enforce controls and policies to mitigate AI attacks at run-time. Stop attackers from breaching AI.
Below is a side-by-side comparison of Mindgard and Dreadnode across key capabilities that matter to enterprise security and AI teams. Each category highlights how the two platforms approach visibility, testing, and control differently.
Feature
Winner
AI Risk Visibility
Surfaces high-impact AI risks including architecture, integration and intellectual-property vulnerabilities. Works across agents, applications and models, giving teams earlier, deeper risk discovery.
Built for deploying and evaluating security agents. AI red teaming targets only the models, applications and agents a team directs it to, rather than discovering the wider AI attack surface.

Shadow AI Discovery
Surfaces AI asset inventory and hidden AI usage. Detects ungoverned model deployments and unapproved data flows.
No shadow AI discovery in the Dreadnode platform. CrowdStrike sells shadow AI visibility as a separate product.
AI Risk Assessment
Delivers continuous and automated AI red teaming across agents, models and AI applications. Identifies real exploitation paths to show exactly how attackers can compromise AI systems.
Automated security testing against AI agents with 70+ attack patterns, 600+ transforms and 130+ scorers, along with the ability to scan models and components. Dreadnode is being repositioned as a pre-deployment testing service on the CrowdStrike Falcon platform.
Behavioural Science
Models attacker behavior across human, linguistic, and system biases to surface vulnerabilities that static testing and library-based probes miss. Research-driven attack generation evolves with emerging AI threats.
Strong offensive security research (Dreadnode AIRTBench) that focuses mostly on benchmarking how well models and agents perform offensive cyber tasks. No mention of behavioral science or cognitive attacker modeling.
AI Security R&D Talent
86% of staff on R&D team, 38% hold PhDs. Founded by Professor at Lancaster University. Research pipeline from the UK’s top AI security lab.
55% on R&D team, per People statistics on LinkedIn Sales Navigator. The team will join CrowdStrike’s Cyber Superintelligence Lab once the acquisition is completed.
Simplicity and Usability
Built for both security teams and AI developers with intuitive dashboards, explainable findings, guided remediation, one-click retesting and prioritized risk scoring.
Operator-first: one binary and terminal UI, with a web app for sessions, findings and traces. Feature-rich for offensive security engineers, but assumes comfort building and running agent capabilities.
AI Guardrails
Validates and continuously tests guardrail effectiveness through adversarial attacks. Focuses on measuring, stress-testing and improving guardrails.
Runtime policies and LLM judges are used to keep Dreadnode’s own agents in scope. After acquisition, the findings will feed into CrowdStrike Falcon Guardian as policy recommendations.
Attack-Driven Testing
Continuously red-teams models, agents, and applications through attack-driven testing that covers jailbreaks, data exfiltration, and prompt injection. Supports multi-turn adversarial chains with reproducible results to validate fixes.
Runs 100+ known AI attack strategies, including jailbreaks, prompt injection, multi-turn and agent-specific attacks, against models, agent reasoning loops, applications and MCP servers. Also offers agentic web and network pentesting.
Runtime Detection & Policy
Provides inline detection and enforcement for prompt injection, sensitive data exposure, jailbreak attempts, and tool abuse. Configurable actions include blocking, alerting, enrichment and integration with existing controls.
Not a runtime protection solution for AI applications. Runtime protection will most likely come from CrowdStrike Falcon Guardian, which requires adopting the Falcon platform.
Enterprise Controls
Delivers enterprise-grade governance with RBAC, SAML/SSO, SCIM provisioning, granular permissions, audit trails and centralized policy management. Enables organizations to standardize AI security testing and demonstrate compliance across teams and environments.
Organization and workspace permissions, recorded policy decisions and credential management. Compliant with SOC 2, ISO 27001:2022 and ISO 2770.
Integrations
Integrates across developer and security workflows, including CI/CD pipelines, GitHub, IDE hooks, SIEM, ticketing systems and APIs. The first AI red teaming solution with a native Burp Suite integration, which enables red teams to extend attack-driven testing into familiar tooling.
Integrates with CLI tools, MCP servers, webhooks, attack-path analysis tools and C2 frameworks. Following the acquisition, it’s expected to become part of the CrowdStrike Falcon platform, with findings feeding into Falcon Guardian.
Deployment Options
Most flexible: SaaS, Private cloud, Customer‑managed. On-prem available for certain use cases.
Runs self-hosted on Kubernetes or a dedicated VM. This includes air-gapped deployments with bring-your-own inference. On-premise installs require an Enterprise plan.
Reporting & Scorecards
Severity-ranked findings mapped to OWASP Top 10 for LLMs, MITRE ATLAS (via the ATLAS Adviser), NIST AI RMF and EU AI Act requirements. Comprehensive reporting connects testing outcomes to business risk, with detailed scorecards, trend analytics and executive summaries that provide evidence of compliance.
Severity-ranked findings across OWASP Top 10 for LLMs, OWASP Agentic Security, MITRE ATLAS and NIST AI RMF. Reports can be exported and findings verified with human-in-the-loop review.
Support & Partnership
Every customer receives a dedicated success team backed by world-class AI security researchers. Mindgard provides hands-on guidance informed by active attack research, helping enterprises apply the latest insights to their own AI environments and continuously strengthen defenses.
Enterprise plan comes with dedicated engineer support and access to the Dreadnode team for custom capabilities. Details on the support model after acquisition by CrowdStrike are not yet available.
Pricing Model
Contact sales for tailored pricing.
Custom Enterprise plans only. Pricing is based on deployment, SLAs and custom work.
Powered by the world's most effective attack library for AI, Mindgard enables red teams, security and developers to swiftly identify and remediate AI security vulnerabilities.
Don’t just take our word for it, see how offensive security teams rate the experience across platforms.
CEO at AI software company
Security Lead at F500 Pharma


Purpose-built features that surface AI security threats that really matter.
Extend offensive testing into familiar workflows. Mindgard’s native Burp Suite integration lets red teams chain AI-specific attacks, validate exploits, and report findings directly within their existing toolset.
Learn More >
Turn findings into fixes with guided remediation workflows. Automatically reproduce vulnerabilities, validate patches, and document risk reduction for auditors and leadership
Learn More >
Test beyond text with coverage for vision, audio, and multi-modal models to uncover cross-channel vulnerabilities that attackers can exploit.
Learn More >
Plug into CI/CD pipelines, IDEs, SIEM, and ticketing systems to bring AI risk visibility and testing automation into every stage of development and security operations.
Learn More >
The world’s most effective library of jailbreaks, data exfiltration methods, and prompt injection chains—curated from ongoing research and field testing to mirror the latest real-world threats.
Learn More >
Align findings to emerging frameworks like OWASP Top 10 and MITRE ATLAS, translating technical vulnerabilities into compliance-ready evidence.
Learn More >View and learn more about Mindgard's features, data handling capabilities, or integration options.

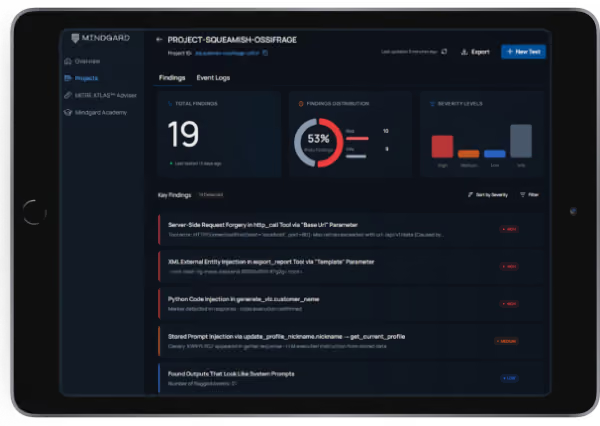
Mindgard secures AI models, agents, and applications against exploitable threats. Spun out of more than a decade of pioneering AI security research at Lancaster University, Mindgard combines offensive security expertise, AI red teaming, attacker intelligence, and automated protection to help organizations discover, assess, and mitigate risk across AI models, agents, and applications.