Webinar: Prompt. Inject. Shell. Repeat - Exploiting Blind Spots within AI Guardrails
AI guardrails are often used as the first line of defense within AI systems, however how effective are they in practice against actual attackers?


UK government commissioned Mindgard to conduct a systematic study to identify recommendations linked to addressing cyber security risks to Artificial Intelligence (AI).
We used a systematic search method to review data sources across multiple domains to identify various recommendations and evidence of cyber risks against AI across academia, technology companies, government bodies, cross-sector initatives (e.g. OWASP), news articles, and technical blogs.
The review also examined common themes and knowledge gaps within AI security remediation actions.
Key findings of the report include:
NIST: “Currently, there is no approach in the field of machine learning that can protect against all the various adversarial attacks.” Continuous automated adversarial testing can help organisations identify emerging weaknesses as AI systems and attack techniques evolve.
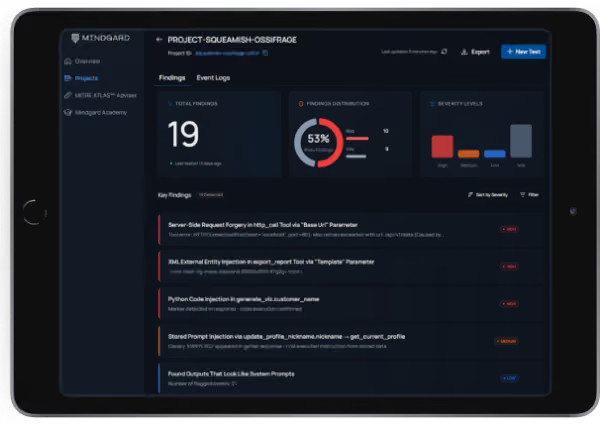
Mindgard helps organizations discover, assess and defend their AI systems. Spun out of more than a decade of AI security research at Lancaster University in the UK and headquartered in Boston and London, Mindgard operationalizes the expertise of AI researchers and offensive security practitioners through a Security Platform that performs Shadow AI discovery, AI red teaming, and run-time AI protection to assess and mitigate risk across models, agents, and applications.